[Aug-2025] Updated ISO 27001 ISO-IEC-27001-Lead-Auditor Exam Questions BUNDLE PACK [Q39-Q62]

4/5 - (1 vote)

[Aug-2025] Updated ISO 27001 ISO-IEC-27001-Lead-Auditor Exam Questions BUNDLE PACK

Master The PECB Content ISO-IEC-27001-Lead-Auditor EXAM DUMPS WITH GUARANTEED SUCCESS!

PECB ISO-IEC-27001-Lead-Auditor exam is a certification program designed to provide individuals with the skills and knowledge necessary to become a certified ISO/IEC 27001 Lead Auditor. ISO-IEC-27001-Lead-Auditor exam is conducted by the Professional Evaluation and Certification Board (PECB), a leading global provider of training, examination, and certification services in the fields of information security, quality management, and business continuity.

PECB ISO-IEC-27001-Lead-Auditor certification exam is highly valued by organizations and employers worldwide as it ensures that the certified professional has the necessary skills and knowledge to perform ISMS audits effectively. It is also an excellent opportunity for professionals to enhance their career prospects and advance their skills in the field of information security management.


NEW QUESTION 39
Scenario 2: Knight is an electronics company from Northern California, US that develops video game consoles. Knight has more than 300 employees worldwide. On the fifth anniversary of their establishment, they have decided to deliver the G-Console, a new generation video game console aimed for worldwide markets. G-Console is considered to be the ultimate media machine of 2021 which will give the best gaming experience to players.
The console pack will include a pair of VR headset, two
games, and other gifts.
Over the years, the company has developed a good reputation by showing integrity, honesty, and respect toward their customers. This good reputation is one of the reasons why most passionate gamers aim to have Knight’s G-console as soon as it is released in the market.
Besides being a very customer-oriented company, Knight
also gained wide recognition within the gaming industry because of the developing quality. Their prices are a bit higher than the reasonable standards allow.
Nonetheless, that is not considered an issue for most loyal customers of Knight, as their quality is top-notch.
Being one of the top video game console developers in the world, Knight is also often the center of attention for malicious activities. The company has had an operational ISMS for over a year. The ISMS scope includes all departments of Knight, except Finance and HR departments.
Recently, a number of Knight’s files containing proprietary information were leaked by hackers. Knight’s incident response team (IRT) immediately started to analyze every part of the system and the details of the incident.
The IRT’s first suspicion was that Knight’s employees used weak passwords and consequently were easily cracked by hackers who gained unauthorized access to their accounts. However, after carefully investigating the incident, the IRT determined that hackers accessed accounts by capturing the file transfer protocol (FTP) traffic.
FTP is a network protocol for transferring files between accounts. It uses clear text passwords for authentication.
Following the impact of this information security incident and with IRT’s suggestion, Knight decided to replace the FTP with Secure Shell (SSH) protocol, so anyone capturing the traffic can only see encrypted data.
Following these changes, Knight conducted a risk assessment to verify that the implementation of controls had minimized the risk of similar incidents. The results of the process were approved by the ISMS project manager who claimed that the level of risk after the implementation of new controls was in accordance with the company’s risk acceptance levels.
Based on this scenario, answer the following question:
FTP uses clear text passwords for authentication. This is an FTP:


NEW QUESTION 40
Information or data that are classified as ______ do not require labeling.


NEW QUESTION 41
Which one of the following options is the definition of an interested party?


NEW QUESTION 42
What controls can you do to protect sensitive data in your computer when you go out for lunch?


NEW QUESTION 43
What is the difference between a restricted and confidential document?


NEW QUESTION 44
What is the standard definition of ISMS?


NEW QUESTION 45
Scenario 3: NightCore is a multinational technology company based in the United States that focuses on e-commerce, cloud computing, digital streaming, and artificial intelligence. After having an information security management system (ISMS) implemented for over 8 months, they contracted a certification body to conduct a third party audit in order to get certified against ISO/IEC 27001.
The certification body set up a team of seven auditors. Jack, the most experienced auditor, was assigned as the audit team leader. Over the years, he received many well known certifications, such as the ISO/IEC 27001 Lead Auditor, CISA, CISSP, and CISM.
Jack conducted thorough analyses on each phase of the ISMS audit, by studying and evaluating every information security requirement and control that was implemented by NightCore. During stage 2 audit. Jack detected several nonconformities. After comparing the number of purchased invoices for software licenses with the software inventory, Jack found out that the company has been using the illegal versions of a software for many computers. He decided to ask for an explanation from the top management about this nonconformity and see whether they were aware about this. His next step was to audit NightCore’s IT Department. The top management assigned Tom, NightCore’s system administrator, to act as a guide and accompany Jack and the audit team toward the inner workings of their system and their digital assets infrastructure.
While interviewing a member of the Department of Finance, the auditors discovered that the company had recently made some unusual large transactions to one of their consultants. After gathering all the necessary details regarding the transactions. Jack decided to directly interview the top management.
When discussing about the first nonconformity, the top management told Jack that they willingly decided to use a copied software over the original one since it was cheaper. Jack explained to the top management of NightCore that using illegal versions of software is against the requirements of ISO/IEC 27001 and the national laws and regulations. However, they seemed to be fine with it.
Several months after the audit, Jack sold some of NightCore’s information that he collected during the audit for a huge amount of money to competitors of NightCore.
Based on this scenario, answer the following question:
Based on scenario 3. which ISO/IEC 27001 control has NightCore ignored when they used an illegal version of software?


NEW QUESTION 46
Which two of the following actions are the individual(s) managing the audit programme responsible for?


NEW QUESTION 47
Scenario 8: EsBank provides banking and financial solutions to the Estonian banking sector since September 2010. The company has a network of 30 branches with over 100 ATMs across the country.
Operating in a highly regulated industry, EsBank must comply with many laws and regulations regarding the security and privacy of dat a. They need to manage information security across their operations by implementing technical and nontechnical controls. EsBank decided to implement an ISMS based on ISO/IEC 27001 because it provided better security, more risk control, and compliance with key requirements of laws and regulations.
Nine months after the successful implementation of the ISMS, EsBank decided to pursue certification of their ISMS by an independent certification body against ISO/IEC 27001 .The certification audit included all of EsBank’s systems, processes, and technologies.
The stage 1 and stage 2 audits were conducted jointly and several nonconformities were detected. The first nonconformity was related to EsBank’s labeling of information. The company had an information classification scheme but there was no information labeling procedure. As a result, documents requiring the same level of protection would be labeled differently (sometimes as confidential, other times sensitive).
Considering that all the documents were also stored electronically, the nonconformity also impacted media handling. The audit team used sampling and concluded that 50 of 200 removable media stored sensitive information mistakenly classified as confidential. According to the information classification scheme, confidential information is allowed to be stored in removable media, whereas storing sensitive information is strictly prohibited. This marked the other nonconformity.
They drafted the nonconformity report and discussed the audit conclusions with EsBank’s representatives, who agreed to submit an action plan for the detected nonconformities within two months.
EsBank accepted the audit team leader’s proposed solution. They resolved the nonconformities by drafting a procedure for information labeling based on the classification scheme for both physical and electronic formats. The removable media procedure was also updated based on this procedure.
Two weeks after the audit completion, EsBank submitted a general action plan. There, they addressed the detected nonconformities and the corrective actions taken, but did not include any details on systems, controls, or operations impacted. The audit team evaluated the action plan and concluded that it would resolve the nonconformities. Yet, EsBank received an unfavorable recommendation for certification.
Based on the scenario above, answer the following question:
Based on scenario 8, EsBank submitted a general action plan. Is this acceptable?


NEW QUESTION 48
You are performing an ISMS audit at a residential nursing home that provides healthcare services. The next step in your audit plan is to verify the information security of the business continuity management process. During the audit, you learned that the organisation activated one of the business continuity plans (BCPs) to make sure the nursing service continued during the recent pandemic. You ask the Service Manager to explain how the organization manages information security during the business continuity management process.
The Service Manager presented the nursing service continuity plan for a pandemic and summarised the process as follows:
Stop the admission of any NEW residents.
70% of administration staff and 30% of medical staff will work from home.
Regular staff self-testing, including submitting a negative test report 1 day BEFORE they come to the office.
Install ABC’s healthcare mobile app, tracking their footprint and presenting a GREEN Health Status QR-Code for checking on the spot.
You ask the Service Manager how to prevent non-relevant family members or interested parties from accessing residents’ personal data when staff work from home. The Service Manager cannot answer and suggests the IT Security Manager should help with that.
You would like to further investigate other areas to collect more audit evidence. Select three options that will not be in your audit trail.


NEW QUESTION 49
AppFolk, a software development company, is seeking certification against ISO/IEC 27001. In the initial phases of the external audit, the certification body in discussion with the company excluded the marketing division from the audit scope, although they stated in their ISMS scope that the whole company is included. Is this acceptable?


NEW QUESTION 50
Scenario 9: Techmanic is a Belgian company founded in 1995 and currently operating in Brussels. It provides IT consultancy, software design, and hardware/software services, including deployment and maintenance. The company serves sectors like public services, finance, telecom, energy, healthcare, and education. As a customer-centered company, it prioritizes strong client relationships and leading security practices.
Techmanic has been ISO/IEC 27001 certified for a year and regards this certification with pride. During the certification audit, the auditor found some inconsistencies in its ISMS implementation. Since the observed situations did not affect the capability of its ISMS to achieve the intended results, Techmanic was certified after auditors followed up on the root cause analysis and corrective actions remotely During that year, the company added hosting to its list of services and requested to expand its certification scope to include that area The auditor in charge approved the request and notified Techmanic that the extension audit would be conducted during the surveillance audit Techmanic underwent a surveillance audit to verify its iSMS’s continued effectiveness and compliance with ISO/IEC 27001. The surveillance audit aimed to ensure that Techmanic’s security practices, including the recent addition of hosting services, aligned seamlessly with the rigorous requirements of the certification The auditor strategically utilized the findings from previous surveillance audit reports in the recertification activity with the purpose of replacing the need for additional recertification audits, specifically in the IT consultancy sector. Recognizing the value of continual improvement and learning from past assessments. Techmanic implemented a practice of reviewing previous surveillance audit reports. This proactive approach not only facilitated identifying and resolving potential nonconformities but also aimed to streamline the recertification process in the IT consultancy sector.
During the surveillance audit, several nonconformities were found. The ISMS continued to fulfill the ISO/IEC 27001*s requirements, but Techmanic failed to resolve the nonconformities related to the hosting services, as reported by its internal auditor. In addition, the internal audit report had several inconsistencies, which questioned the independence of the internal auditor during the audit of hosting services. Based on this, the extension certification was not granted. As a result. Techmanic requested a transfer to another certification body. In the meantime, the company released a statement to its clients stating that the ISO/IEC 27001 certification covers the IT services, as well as the hosting services.
Based on the scenario above, answer the following question:
According to Scenario 9, the auditor decided to conduct the extension audit during the surveillance audit. How do you define this situation?


NEW QUESTION 51
Scenario 4: SendPay is a financial company that provides its services through a network of agents and financial institutions. One of their main services is transferring money worldwide. SendPay, as a new company, seeks to offer top quality services to its clients. Since the company offers international transactions, it requires from their clients to provide personal information, such as their identity, the reason for the transactions, and other details that might be needed to complete the transaction. Therefore, SendPay has implemented security measures to protect their clients’ information, including detecting, investigating, and responding to any information security threats that may emerge. Their commitment to offering secure services was also reflected during the ISMS implementation where the company invested a lot of time and resources.
Last year, SendPay unveiled their digital platform that allows money transactions through electronic devices, such as smartphones or laptops, without requiring an additional fee. Through this platform, SendPay’s clients can send and receive money from anywhere and at any time. The digital platform helped SendPay to simplify the company’s operations and further expand its business. At the time, SendPay was outsourcing its software operations, hence the project was completed by the software development team of the outsourced company.
The same team was also responsible for maintaining the technology infrastructure of SendPay.
Recently, the company applied for ISO/IEC 27001 certification after having an ISMS in place for almost a year. They contracted a certification body that fit their criteria. Soon after, the certification body appointed a team of four auditors to audit SendPay’s ISMS.
During the audit, among others, the following situations were observed:
1.The outsourced software company had terminated the contract with SendPay without prior notice. As a result, SendPay was unable to immediately bring the services back in-house and its operations were disrupted for five days. The auditors requested from SendPay’s representatives to provide evidence that they have a plan to follow in cases of contract terminations. The representatives did not provide any documentary evidence but during an interview, they told the auditors that the top management of SendPay had identified two other software development companies that could provide services immediately if similar situations happen again.
2.There was no evidence available regarding the monitoring of the activities that were outsourced to the software development company. Once again, the representatives of SendPay told the auditors that they regularly communicate with the software development company and that they are appropriately informed for any possible change that might occur.
3.There was no nonconformity found during the firewall testing. The auditors tested the firewall configuration in order to determine the level of security provided by these services. They used a packet analyzer to test the firewall policies which enabled them to check the packets sent or received in real-time.
Based on this scenario, answer the following question:
SendPay’s representatives stated that the company did not have a plan to follow in case of a contract termination with the company that they outsource activities to. Instead, the top management had identified two other software development companies that could provide the same services. How do you describe this situation?


NEW QUESTION 52
You are an experienced audit team leader guiding an auditor in training.
Your team is currently conducting a third-party surveillance audit of an organisation that stores data on behalf of external clients. The auditor in training has been tasked with reviewing the PHYSICAL controls listed in the Statement of Applicability (SoA) and implemented at the site.
Select four controls from the following that would you expect the auditor in training to review.


NEW QUESTION 53
You are an experienced audit team leader guiding an auditor in training.
Your team is currently conducting a third-party surveillance audit of an organisation that stores data on behalf of external clients. The auditor in training has been tasked with reviewing the PEOPLE controls listed in the Statement of Applicability (SoA) and implemented at the site.
Select four controls from the following that would you expect the auditor in training to review.


NEW QUESTION 54
Scenario 7: Lawsy is a leading law firm with offices in New Jersey and New York City. It has over 50 attorneys offering sophisticated legal services to clients in business and commercial law, intellectual property, banking, and financial services. They believe they have a comfortable position in the market thanks to their commitment to implement information security best practices and remain up to date with technological developments.
Lawsy has implemented, evaluated, and conducted internal audits for an ISMS rigorously for two years now. Now, they have applied for ISO/IEC 27001 certification to ISMA, a well-known and trusted certification body.
During stage 1 audit, the audit team reviewed all the ISMS documents created during the implementation. They also reviewed and evaluated the records from management reviews and internal audits.
Lawsy submitted records of evidence that corrective actions on nonconformities were performed when necessary, so the audit team interviewed the internal auditor. The interview validated the adequacy and frequency of the internal audits by providing detailed insight into the internal audit plan and procedures.
The audit team continued with the verification of strategic documents, including the information security policy and risk evaluation criteri a. During the information security policy review, the team noticed inconsistencies between the documented information describing governance framework (i.e., the information security policy) and the procedures.
Although the employees were allowed to take the laptops outside the workplace, Lawsy did not have procedures in place regarding the use of laptops in such cases. The policy only provided general information about the use of laptops. The company relied on employees’ common knowledge to protect the confidentiality and integrity of information stored in the laptops. This issue was documented in the stage 1 audit report.
Upon completing stage 1 audit, the audit team leader prepared the audit plan, which addressed the audit objectives, scope, criteria, and procedures.
During stage 2 audit, the audit team interviewed the information security manager, who drafted the information security policy. He justified the Issue identified in stage 1 by stating that Lawsy conducts mandatory information security training and awareness sessions every three months.
Following the interview, the audit team examined 15 employee training records (out of 50) and concluded that Lawsy meets requirements of ISO/IEC 27001 related to training and awareness. To support this conclusion, they photocopied the examined employee training records.
Based on the scenario above, answer the following question:
The audit team photocopied the examined employee training records to support their conclusion. Should the audit team obtain an approval from Lawsy before taking this action? Refer to scenario 7.


NEW QUESTION 55
Your organisation is currently seeking ISO/IEC27001:2022 certification. You have just qualified as an Internal ISMS auditor and the ICT Manager wants to use your newly acquired knowledge to assist him with the design of an information security incident management process.
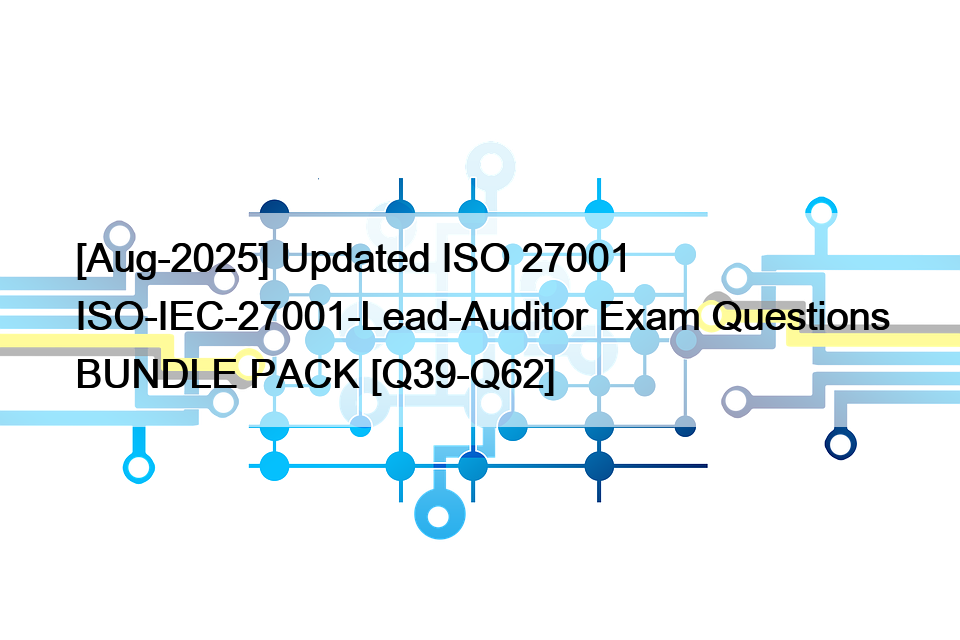
He identifies the following stages in his planned process and asks you to confirm which order they should appear in.

NEW QUESTION 56
EquiBank is undergoing an external audit of its financial management system. The auditors evaluate the logic of transactions processed by EquiBank’s financial software. To ensure accuracy, they use simulations to validate operations, calculations, and controls programmed in the software applications. What type of Computer-Assisted Audit Technique (CAAT) is used?


NEW QUESTION 57
You are an experienced ISMS auditor, currently providing support to an ISMS auditor in training who is carrying out her first initial certification audit. She asks you what she should be verifying when auditing an organisation’s Information Security objectives. You ask her what she has included in her audit checklist and she provides the following replies.
Which three of these responses would you cause you concern in relation to conformity with ISO/IEC
27001:2022?


NEW QUESTION 58
Your organisation is currently seeking ISO/IEC27001:2022 certification. You have just qualified as an Internal ISMS auditor and the ICT Manager wants to use your newly acquired knowledge to assist him with the design of an information security incident management process.
He identifies the following stages in his planned process and asks you to confirm which order they should appear in.

NEW QUESTION 59
You are performing an ISMS audit at a nursing home where residents always wear an electronic wristband for monitoring their location, heartbeat, and blood pressure. The wristband automatically uploads this data to a cloud server for healthcare monitoring and analysis by staff.
You now wish to verify that the information security policy and objectives have been established by top management. You are sampling the mobile device policy and identify a security objective of this policy is “to ensure the security of teleworking and use of mobile devices” The policy states the following controls will be applied in order to achieve this.
Personal mobile devices are prohibited from connecting to the nursing home network, processing, and storing residents’ data.
The company’s mobile devices within the ISMS scope shall be registered in the asset register.
The company’s mobile devices shall implement or enable physical protection, i.e., pin-code protected screen lock/unlock, facial or fingerprint to unlock the device.
The company’s mobile devices shall have a regular backup.
To verify that the mobile device policy and objectives are implemented and effective, select three options for your audit trail.


NEW QUESTION 60
What is the name of the system that guarantees the coherence of information security in the organization?


NEW QUESTION 61
The following are purposes of Information Security, except:


NEW QUESTION 62
You receive an E-mail from some unknown person claiming to be representative of your bank and asking for your account number and password so that they can fix your account. Such an attempt of social engineering is called


Pass PECB ISO-IEC-27001-Lead-Auditor Exam – Experts Are Here To Help You: https://www.validexam.com/ISO-IEC-27001-Lead-Auditor-latest-dumps.html


Related Links: www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw findaspring.org

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below